ChatGPT: Correctly Checking for Phishing Email Analysis

I gave ChatGPT the same suspicious Microsoft 365 email that Gemini had analyzed incorrectly. ChatGPT recognized the message as a Microsoft-generated malware rejection notice. After I supplied the original headers, the evidence confirmed its conclusion: an outside server had spoofed a CharlesWorks address while Microsoft successfully blocked a malicious SVG attachment.

My ChatGPT Phishing Email Analysis

As I had mentioned in the last post, I noticed what I thought was a phishing email in my Inbox. This time, I did a ChatGPT phishing email analysis.

I always share that I like using Microsoft Outlook web mail for my Office 365 account. Having been in the web business in excess of 28 years I am most confident saying it is the most secure 🔐 email to use for one’s business or personal connecting. Whether you are running a business or use email only for personal use, security is a must because our email is tied to many aspects of our lives.

When I see a phishing or otherwise bad actor originated email that perplexes me, I investigate it to learn more about it. This is important to me because one of my purposes in life is to help my web clients avoid what can be difficult issues to avoid concerning their email.

Gemini Result Was Just Way Off Base

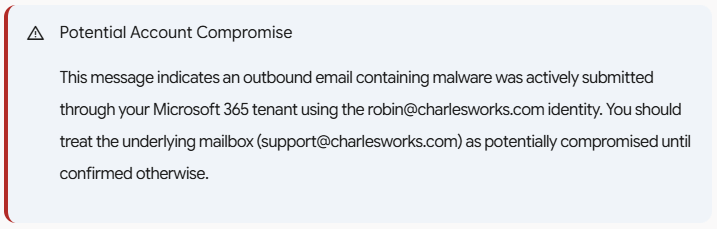
I was taken aback with my Gemini result posted in the last post. It warned me that my account should be treated as potentially compromised until confirmed otherwise. Again, I would say this is normally good advise – to always prove the account is safe when in doubt. However, it is an expensive endeavor when – like most of my web clients – one has to hire a firm like ours or an IT firm to go through the necessary steps to investigate.

The output from Gemini proved what all the AI outputs usually indicate: that they can be wrong. Gemini’s outlput also pointed out the importance of what I would choose: a second opinion. My second opinions usually come in the form of using one or more separate AIs to examine a problem of this nature. If they all agree, great! When two out of three agree, that’s still a good indication. But if none agreed, I’m probably not asking the right question.

The most important thing I learned in my master’s degree studies: it’s all about knowing the right questions to ask.

Here is exactly what I asked ChatGPT followed by its confirmed correct assessment and followup info I provided it. Note that ChatGPT asked for more information based in its suspicions. My experience in these matters verifies its behavior based on what I would have done:

I am trying to find out where this message came from and why it ends up in my Inbox. I use Outlook web mail and I believe it may be a phishing message but the option to “Report” it as either spam or phishing do not show up when I right click on it (although that option shows on other emails). It indicates it was sent by ro***@**********ks.com but there is only an alias for ro***@**********ks.com to su*****@**********ks.com and mail could not have been sent from that nonexistent address:
This message was created automatically by mail delivery software. Your email message was not delivered to the intended recipients because malware was detected.
— Additional Information —:
Subject: -Caller left 34s September 19, 2026 – cJIBRTd8.
Sender: ro***@**********ks.com
Time received: 9/19/2026 4:10:15 AM
Message ID:<[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>
Detections found:
Vrecording_Erecorded_ATT61.svg..        Script/SvgStealer.ADX!MTB
The “view Massage” option in my Outlook web mail shows me this:
Received: from PH8PR11MB7024.namprd11.prod.outlook.com (2603:10b6:510:220::19)
 by SAVPR11MB9574.namprd11.prod.outlook.com with HTTPS; Sat, 19 Sep 2026
 04:10:18 +0000
Received: from SmtpServer.Submit by PH8PR11MB7024 with Microsoft SMTP Server
 id 15.21.406.11; Sat, 19 Sep 2026 04:10:18 +0000
MIME-Version: 1.0
Content-Type: text/plain; charset=”utf-8″
From: Postmaster <po********@**********ks.com>
Subject: Undeliverable message
Content-Transfer-Encoding: quoted-printable
To: <su*****@**********ks.com>
Message-ID:
 <7f**********************************@*********************************ok.com>
Return-Path: po********@**********ks.com
Date: Sat, 19 Sep 2026 04:10:18 +0000
X-MS-Exchange-Organization-ExpirationStartTime: 19 Sep 2026 04:10:18.2837
 (UTC)
X-MS-Exchange-Organization-ExpirationStartTimeReason: OriginalSubmit
X-MS-Exchange-Organization-ExpirationInterval: 1:00:00:00.0000000
X-MS-Exchange-Organization-ExpirationIntervalReason: OriginalSubmit
X-MS-Exchange-Organization-Network-Message-Id:
 29b93226-d43b-478f-fcd1-08df1603ea60
X-MS-Exchange-Organization-AuthSource: PH8PR11MB7024.namprd11.prod.outlook.com
X-MS-Exchange-Organization-AuthAs: Internal
X-MS-Exchange-Organization-AuthMechanism: 05
X-MS-Exchange-Parent-Message-Id:
 <[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>
Auto-Submitted: auto-generated
X-MS-Exchange-Generated-Message-Source: DC Post Content Filter Agent
X-MS-PublicTrafficType: Email
X-MS-TrafficTypeDiagnostic: PH8PR11MB7024:EE_|SAVPR11MB9574:EE_
X-MS-Exchange-Organization-SCL: 1
X-Microsoft-Antispam:
 BCL:0;ARA:13230040|1930700014|366016|56012099006|12063799003|10067099003|18002099003|41050700001;
X-Forefront-Antispam-Report:
 CIP:255.255.255.255;CTRY:;LANG:en;SCL:1;SRV:;IPV:NLI;SFV:NSPM;H:;PTR:;CAT:NONE;SFS:(13230040)(1930700014)(366016)(56012099006)(12063799003)(10067099003)(18002099003)(41050700001);DIR:INT;
X-MS-Exchange-CrossTenant-OriginalArrivalTime: 19 Sep 2026 04:10:18.2834 (UTC)
X-MS-Exchange-CrossTenant-Network-Message-Id:
 29b93226-d43b-478f-fcd1-08df1603ea60
X-MS-Exchange-CrossTenant-AuthSource: PH8PR11MB7024.namprd11.prod.outlook.com
X-MS-Exchange-CrossTenant-AuthAs: Internal
X-MS-Exchange-CrossTenant-FromEntityHeader: Hosted
X-MS-Exchange-Transport-CrossTenantHeadersStamped: PH8PR11MB7024
X-MS-Exchange-Organization-MessageDirectionality: Originating
X-MS-Exchange-Transport-EndToEndLatency: 00:00:00.6486099
X-MS-Exchange-Processed-By-BccFoldering: 15.21.0428.008
X-MS-Exchange-ExternalInOutlookResult: NotEnabled
X-Microsoft-Antispam-Mailbox-Delivery:
ucf:0;jmr:0;auth:0;dest:I;ENG:(910005)(944506478)(944626604)(920097)(425001)(930201)(20251009189)(140003);
X-Microsoft-Antispam-Message-Info:
xuNr8XT2UiI8kmeQ7vTwjjloBhzPu/NOSnDZ8nYwnyjaERxMG5YzKr35E2fY/Ja+bMQAd9LPy0fbIn9ejg8cTQVMmPfNLeEQ2Krgx1F6DxdeAufyJfN0jjFjkgr4eUrr2/bahM6aMBHXalIKcAy0HqlN100CggPEgGABIWOyuhttlvvX/Tdl0OViDHgOtPw9lCUi1vx3u/zwNovLrZltOsoVBKT/yggFMCquH/6gm1d95gnQwZhhRUYH/lVN/UZfdx1XLWUt3eaO5VMl0CHnw/MKpu8dDHsYtn9u89Q1Zk8lS0MPCxKuuvBkGfobsYvR+kOsCf7+Arz/ltMO99w5DuocxkuDLLFNO4DfSWRkw+Ovm2XBelFakkrv0WHSK4q+08Allgeox1hWGEIeknDBwIWj0t6JkmiqIW3FWVhFzFqArsBfbqZaxGWo3PZOFgTBpRoALq3aJ86kISw1OZVs9IBDZYht0367UoWe0GImW808FeuiC1efb1Emfx686OW0NddoP36TMqjiEaOBKCrkSklyc1Gk7wEPX1vDGA+u0tCkEnOl3Pj/aqaQqXwirS9F0ZTRdRwUxpS6SR0fb3IRUdcGG++r8+BxYwHa1vOSlSC8u8/Gy1ZJIK/fxdcp2A35orzJRsFY4ftB+TK5nYos5allhlQdZEzdYMeD/nbof0pj81gJ/Z1dCCgVXF8NicNIJAlgFMbkCDqPRay9qsAhg4zM/bXaghQAqwCw1PpGHnOn0oetsOiyqpNJpj9SVGvSIRJT2T6bVN0m/pjRXFujF8cwU+AZq6wPtCxvdRodrAX63c4ZUjcykjCZmsC9I7fL
OpenAI ChatGPT LogoWhat you are seeing is not the original malicious message. It is a Microsoft Exchange Online-generated delivery failure notice created after Microsoft detected malware in another message.

Several headers make that clear:

  • From: Postmaster <po********@**********ks.com>
  • X-MS-Exchange-Organization-AuthAs: Internal
  • X-MS-Exchange-Organization-MessageDirectionality: Originating
  • X-MS-Exchange-Generated-Message-Source: DC Post Content Filter Agent
  • Auto-Submitted: auto-generated

So the message sitting in your Inbox was generated inside Microsoft’s mail system. That also explains the odd behavior you’re seeing in Outlook.

Why “Report phishing” is missing

Microsoft considers this particular message an internal system-generated notification, not an Internet email.

These headers reinforce that:

X-MS-Exchange-Organization-SCL: 1
SFV:NSPM
DIR:INT

SCL: 1 is a very low spam score, NSPM means Microsoft’s filter classified it as not spam, and DIR:INT identifies the delivery as internal.

Consequently, Outlook apparently isn’t offering you the normal Report → Junk / Phishing choices. There really isn’t much point in reporting this particular message anyway—the malicious message was the parent message, and Microsoft already caught it.

The interesting part is ro***@**********ks.com

The important distinction is this:

An email absolutely can claim to be from ro***@**********ks.com even though no mailbox named Robin exists.

SMTP does not require the address in the sender field to correspond to a real mailbox. A spammer can send something like:

MAIL FROM:<ro***@**********ks.com>
From: ro***@**********ks.com

from a server anywhere in the world.

The fact that ro***@**********ks.com is an alias of su*****@**********ks.com explains very nicely why the resulting failure notice wound up with:

To: <su*****@**********ks.com>

Microsoft attempted to return the failure notice to the purported sender, ro***@**********ks.com. Since Microsoft 365 knows that address belongs to the support mailbox, the notification wound up in support’s Inbox.

In other words, this has all the hallmarks of backscatter caused by a spoofed sender address.

The SVG malware is another big clue

The blocked parent message had:

Subject: -Caller left 34s September 19, 2026 - cJIBRTd8.

and Microsoft found:

Vrecording_Erecorded_ATT61.svg
Script/SvgStealer.ADX!MTB

That looks very much like the current style of fake voicemail/call recording phishing lure. The .svg attachment contained scripting Microsoft classified as credential-stealing malware.

So I would not open or attempt to recover that attachment.

But we can determine where the original message really came from

The NDR fortunately gives us the original message ID:

<[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>

It appears again here:

X-MS-Exchange-Parent-Message-Id:

That gives us something very useful to hunt down in your Microsoft 365 message trace.

Go to:

https://admin.exchange.microsoft.com/

Then go to Mail flow → Message trace.

I’d search a window around:

September 19, 2026, 04:10 UTC

which is September 19, 2026, 12:10 AM Eastern Daylight Time.

First try:

Sender:
ro***@**********ks.com

and leave the recipient unrestricted if Exchange lets you.

I’d use perhaps 04:00 through 04:20 UTC to keep the results small.

What we want to see

If the trace shows something equivalent to an incoming Internet message with a remote sending IP, then we’ve nailed it:

Someone on the Internet spoofed ro***@**********ks.com, Microsoft detected malware, generated an NDR to the spoofed sender, and because Robin is an alias of Support, you received the NDR.

That is what I presently think happened.

However, if the trace shows that the parent message was submitted/authenticated within your Microsoft 365 organization, that becomes much more interesting. Then we would want to determine whether it came from:

  • the support mailbox using the Robin alias,
  • an authenticated SMTP client,
  • a Microsoft 365 account,
  • an application,
  • a connector,
  • or another authorized sending mechanism.

I do not see evidence in the headers you’ve provided that the Robin account was compromised. In fact, since Robin isn’t an account, that particular scenario makes little sense. The AuthAs: Internal header applies to the NDR you’re reading, not necessarily to the malicious parent message. That’s an important distinction.

So my working theory is:

Internet attacker → spoofed ro***@**********ks.com → malicious fake voicemail message → Microsoft malware filter catches it → Microsoft sends failure notice back to Robin → Robin alias resolves to Support → NDR lands in your Inbox.

If you give me the message trace details for the parent message, we should be able to prove or disprove that theory and, hopefully, identify the actual sending IP.

Received: from BN9PR03CA0851.namprd03.prod.outlook.com (2603:10b6:408:13d::16)

by PH8PR11MB7024.namprd11.prod.outlook.com (2603:10b6:510:220::19) with

Microsoft SMTP Server (version=TLS1_2,

cipher=TLS_ECDHE_RSA_WITH_AES_256_GCM_SHA384) id 15.21.406.11; Sat, 19 Sep

2026 04:10:15 +0000

Received: from BN2PEPF0000A894.namprd04.prod.outlook.com

(2603:10b6:408:13d:cafe::20) by BN9PR03CA0851.outlook.office365.com

(2603:10b6:408:13d::16) with Microsoft SMTP Server (version=TLS1_3,

cipher=TLS_AES_256_GCM_SHA384) id 15.21.428.13 via Frontend Transport; Sat,

19 Sep 2026 04:10:15 +0000

Authentication-Results: spf=none (sender IP is 192.3.183.94)

smtp.helo=mta-80-125.sparkpostmail.com; dkim=none (message not signed)

header.d=none;dmarc=fail action=quarantine

header.from=charlesworks.com;compauth=fail reason=000

Received-SPF: None (protection.outlook.com: mta-80-125.sparkpostmail.com does

not designate permitted sender hosts)

Received: from mta-80-125.sparkpostmail.com (192.3.183.94) by

BN2PEPF0000A894.mail.protection.outlook.com (10.167.248.186) with Microsoft

SMTP Server (version=TLS1_3, cipher=TLS_AES_256_GCM_SHA384) id 15.21.451.8

via Frontend Transport; Sat, 19 Sep 2026 04:10:15 +0000

Return-Path: <>

From: ro***@**********ks.com

To: Robin <ro***@**********ks.com>

Subject: -Caller left 34s September 19, 2026 – cJIBRTd8.

Message-ID: <[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>

Date: Sat, 19 Sep 2026 04:10:14 +0000

MIME-Version: 1.0

Content-Type: text/plain

X-EOPAttributedMessage: 0

X-EOPTenantAttributedMessage: 87733afe-0d9d-4701-bcd1-865bd5674a0b:0

X-MS-PublicTrafficType: Email

X-MS-TrafficTypeDiagnostic: BN2PEPF0000A894:EE_

PH8PR11MB7024:EE_

X-MS-Office365-Filtering-Correlation-Id: de0283ca-ed7e-4553-f9b1-08df1603e88e

X-MS-Exchange-AtpMessageProperties: SA

SL

X-Forefront-Antispam-Report: CIP:192.3.183.94;CTRY:US;LANG:en;SCL:9;SRV:;IPV:NLI;SFV:SPM;H:mta-80-125.sparkpostmail.com;PTR:192-3-183-94-host.colocrossing.com;CAT:AMP;SFS:(13230040)(5009299003)(6049299003)(29132699027)(260918215300599003)(260918224100599003)(5063699009)(10067099003)(18002099003)(55112099003)(19002099009)(4053099003)(57112099003);DIR:INB;

X-Microsoft-Antispam: BCL:0;ARA:13230040

5009299003

6049299003

29132699027

260918215300599003

260918224100599003

5063699009

10067099003

18002099003

55112099003

19002099009

4053099003

57112099003;

X-Microsoft-Antispam-Message-Info: =?us-ascii?Q?6hEd90HgmiMpox31IEQxVxzcBToOab3qD3knO+p3n5bIHQyfxQ9uiHWVCRl2?=

=?us-ascii?Q?gq2BEwBVxpEF1SFdx5uujuYSw1aqU14WB2OgQnVz6hHBW+ZB6/tEUyTAvOAj?=

=?us-ascii?Q?ctZmS9QioFJ/dqnLulvOdr6cx7D+ub7MOzgX+TD3vc/n/xgjMdqMdkl8UTWC?=

=?us-ascii?Q?WI5XYa9Ec9+9ybXxz1lKFBqbF9ETYtj7jAYgbwxQet6DUoqOv1gn6/azfF+U?=

=?us-ascii?Q?sGv198ljoKLBMQEZsK1aPgAMKC/k5TbmPjSav9pLar1ulwnMKkcq/P75HiO2?=

=?us-ascii?Q?mMIFPBJ71LWAdHE2vAnrWuH2tP9JmpOwSM3/TRzprcEJJA6py8JK+eHF5mPX?=

=?us-ascii?Q?83JTV2+jTBcKsQURERAZdonS8izIBAfTQ930VKQFylFeF46EMlEzsdn4GoZN?=

=?us-ascii?Q?8lv9KjRT8tAvEhsC8wYEDTXRhIhenEqK8e+m52PlV2jWyT8deEcCAtUNc0lB?=

=?us-ascii?Q?KT0S85AgvGAdMJPTdMMmQrkElN/6faU68PbTr/pUjVurxn9Flgiy0AqsIwsN?=

=?us-ascii?Q?HhnuHJXljMc0CnFtnzc0fziXucrdVH2mgoI0+Ug++UL0lZHxMeMPoe97TaWi?=

=?us-ascii?Q?W+F86blHHdZmG/oIDvhVNNbTFpceeuUaZ0YUUWOuKCsgwCWE4CA4v7Wkc6R2?=

=?us-ascii?Q?k7Mf6DZX1dg1RZa99RPb7THWob4Opc+uQQw2rxgrA6Ud1LfKFvyIlk5A4O6Z?=

=?us-ascii?Q?oJBTbEVcsKgjPHNwe18ssQ6O2Ol+KKEB1KT5oCFdmN2Z3b/0w+2VFI2O1z4N?=

=?us-ascii?Q?Sgr/4oF4vh/ERn073CGS8jyzUprS1eE+NtDaanx3tznTA37163ZqEzudtb9d?=

=?us-ascii?Q?Ual9i88maSy0JY91Nq4m/jTnvn1Kkyn+RCxRSfJhcRIqVSFX5Nm5o9u4HXNq?=

=?us-ascii?Q?cP05yaUaI0gO8K84pjjF7egluzXz1JCC1QsPswmJX72RP3pH8CLbblHhP+/n?=

=?us-ascii?Q?xYVKhgQmPO/eiHL1UNr9bgiSsiuADME9YHhoy6ZB8MLrZcXTP60TfNmVDZmo?=

=?us-ascii?Q?l0A6J96y+ZTzk5AqJFfGkjYdhUXENPYKAg/SHJmAddtjpZDViWYx0IHls0sR?=

=?us-ascii?Q?eJzoSIvlaZY56vpR+g3lQFYngSFj5hGxQsuLXysbPv2/FqBHuSyEL5OVAkOj?=

=?us-ascii?Q?2OofuOk3tiTXDIxFoNroW9t4IYUNCsfDTkTZxbVWlR0XTk5LJ2t9ZpXgOr1g?=

=?us-ascii?Q?8o9gIZrPavC8bKNwVBJnsGM+FGEKV4OZkAFMzppE/Z0/Umx4gEImb9YGLb9M?=

=?us-ascii?Q?GnPoOJS7WDorecCX8qw2I8TI086Hn+poi6X4JyRvkyqEifb0tB3s33QghwrH?=

=?us-ascii?Q?mge2524Lx4RzDPLl1frWq1hGZl5ll0X+TsgN7n6kmLgXAnSpJxkIHM0RKk+1?=

=?us-ascii?Q?Cqj/4ycJoHCG/RgugkM8YBS0WH/OUlKjtwuI800e1N6MxmkM2skPqzLq1Knh?=

=?us-ascii?Q?ubFxcE8cu2DZsNU7MbdqRDJRUenCn5VunfoPrl/wEsPE05i/LC0KXBlsmfhL?=

=?us-ascii?Q?jVZ9p4IimaP992ComQKeIPJhge5T8kInCKF6yMz0bFD28w7GalqDxEhtIfd1?=

=?us-ascii?Q?p7HMsPq66nJ66nnfgZ5RqWITjJzgu9PJid/MgwZ9uDDWgV8wNeDRuqNc8Hhh?=

=?us-ascii?Q?+S2fq8D/bJXhEB3Dg/EeOnCor9yHWePnfQG8xoVoVEsgtbldqqhOKlWufygX?=

=?us-ascii?Q?rHSQFtyIJQjDWXon/eHbvU4Idrm5sQzUuZQfmD184HdI+SLowM2bf84omXt0?=

=?us-ascii?Q?przsy2LAIyQu096JAYs6rM0MSXKGGXi6W4g00+DmsHdQ5E+ni0aC7jnYSX2O?=

=?us-ascii?Q?lJ+gBBbokqdlOz0UOu3pY2GxA6icRLYkY/rln8ITagHemAGOMgq/8byYcluj?=

=?us-ascii?Q?UFgaittHWJGhPbNF3iVcztwAVytozBswA5FIzwt/2UJiOoFj0ai6YE9ipMjR?=

=?us-ascii?Q?9Y8zGQRB2l3jMYHiFdT1cCiG/TlGirNQmAJsWg037Kh1ui0VQ6tu1Y2fZjQF?=

=?us-ascii?Q?JHjMpzBJCCA4O9zc9oviFrUEiDR29j74DPrhQivj5VjQvI1ctXl8P02T71CI?=

=?us-ascii?Q?aQ8XV0lUHdTwD28moXEOLPV3I1u4Tk3F5zHZ3GK+mje1c5gbkObTFQtlbUkA?=

=?us-ascii?Q?RdfPN2GfpJm75gJoIJVkgsUgvDsHOl0jSN/eo7F7b0Rr3e/PlVvxdLCgBh5M?=

=?us-ascii?Q?I9P9B8a5nzDcNoy6XbRKvQO0a8KKOqHnG+rBBuUy0Kpx+I8Y02BJabtaSbXa?=

=?us-ascii?Q?i1Kr8qHKMAJgNRVpOVKqK8Q4WxuPXr160g3kabt6o8jLQ1T5t7sn6WwyrLov?=

=?us-ascii?Q?hAW8aKfdABmRoBBH8KKB1JwdpKsQNO2DhxGJfDnfAuu2llp5VCMsthsQN/pW?=

=?us-ascii?Q?xtcOOeEo3rhoEm8RA7EzJxb3z9oeu9r3neXWFaOiocMcFRM6AdhwanetLJk+?=

=?us-ascii?Q?3xrcVfcuDhesBSRZDeE/pS/ngjvJHKlko/Ck2x3rxpAP6L6v6T++/5DsUBU4?=

=?us-ascii?Q?fDmZ3zSu0mWOP1aet12G6EPzqFv9wKjC2zv1FYGUHfqZht8+DC8icsaqa1xa?=

=?us-ascii?Q?y4zVW12aZs/GyHP5M6WD7oOQfqzLv24+4yJsvHV8+hZ27V5y9uqrcBHvEAA/?=

=?us-ascii?Q?ZmHS0ALpVPEIhP+8yQRakhTxhkA01Di9ARBIiGvEj2Yj2K2BZTjp0HkIbhJJ?=

=?us-ascii?Q?uvAZhhPVlarQIIdJSnrL2q83+bBPnmCB1gbrOkos0T06Lpb99t9QEWNvA7EV?=

=?us-ascii?Q?4kWt4cbqW4GW6iRIQ+GES55392EqFA3EqP7TU87osxGD6h2d4OLawyyhW+d0?=

=?us-ascii?Q?/w1Y0ih4dsXU9fwv/36ny3aDOKbUUdUbx1v9FzS+T5QPdM6E6k8Xin8YlAss?=

=?us-ascii?Q?U6BQMgbc0VVaHcITcBDpMjMqj62sfIoaSTVgMYnGqBmikL1NjjyaKXhlTolT?=

=?us-ascii?Q?i3N9OSFXLdkJqfz+0PRGYCnGnmYhIE5mot59tZKpYFYV07EqiVPiysz1XPSs?=

=?us-ascii?Q?2bB+llvUIXF9Y3ZixNAMsn8h/2ysR3OGtv4kom0f6jAOFYrB2iydtQRstvRA?=

=?us-ascii?Q?A/bxa2BRSr1/CQqk1jK+DLb0ibBreZYn2fC+gZpUqTqRZtQC3a6KGeVq58JS?=

=?us-ascii?Q?NRF7DFUaE7QGFBamrnsbGIFFWlV/cj4UIm7LY5LPnDgdKlSPkHPjDZ/mx83b?=

=?us-ascii?Q?ZlrZr+vxULHgV47zQnLN/T1y6IbAoHfmVnwtZA=3D=3D?=

Yes. This second set of headers proves it.

The message was spoofed, and it did not originate from ro***@**********ks.com, Outlook, Microsoft 365, or any CharlesWorks mail server.

The actual Internet host that connected to Microsoft was:

192.3.183.94

at 04:10:15 UTC on September 19, 2026.

The smoking-gun line is:

Received: from mta-80-125.sparkpostmail.com (192.3.183.94)
 by BN2PEPF0000A894.mail.protection.outlook.com

But even the mta-80-125.sparkpostmail.com name is misleading. That’s the hostname the connecting SMTP server announced in its HELO/EHLO. The reverse DNS Microsoft actually found was:

PTR:192-3-183-94-host.colocrossing.com

And the 192.3.183.0/24 network is currently associated with AS36352/HostPapa infrastructure. (IPinfo)

Even more striking: Sublime Security documented this exact same IP, 192.3.183.94, on January 6, 2026, sending malicious SVG credential-phishing messages disguised as voicemail notifications. Their specimen spoofed a GoDaddy address, failed SPF and DMARC, and came from this exact IP. (sublime.security)

Their description of another attack from the same infrastructure is almost a word-for-word match for yours: voicemail language, a malicious .svg attachment containing JavaScript, SPF/DMARC failure, and identical sender/recipient addresses. (sublime.security)

So this is not merely “probably phishing.” You’ve caught a known attack pattern coming from an IP previously documented distributing essentially the same malicious voicemail/SVG campaign. I wouldn’t claim we know it’s the identical attacker—the IP could be reused—but the infrastructure and technique match remarkably closely.

Your Microsoft headers also make the spoofing completely explicit:

Authentication-Results:
 spf=none (sender IP is 192.3.183.94)
 smtp.helo=mta-80-125.sparkpostmail.com;
 dkim=none (message not signed)
 header.d=none;
 dmarc=fail action=quarantine
 header.from=charlesworks.com;
 compauth=fail

In plain English:

SPF:       FAILS to authenticate CharlesWorks
DKIM:      NO CharlesWorks signature
DMARC:     FAIL
CompAuth:  FAIL
Direction: INBOUND from Internet
Spam:      SCL 9 — extremely high

And this header is especially important:

DIR:INB

That’s Microsoft’s designation for inbound Internet mail. So there is no possibility here that Robin somehow sent it through your Microsoft 365 organization.

What actually happened

The sequence appears to be:

Attacker-controlled server
192.3.183.94
        |
        | claimed HELO:
        | mta-80-125.sparkpostmail.com
        v
Microsoft 365 Protection
        |
        | From: ro***@**********ks.com   <-- FORGED
        | To:   ro***@**********ks.com
        |
        | SPF:   none
        | DKIM:  none
        | DMARC: FAIL
        | SCL:   9
        |
        | Malware detected in SVG
        X
   MESSAGE BLOCKED
        |
        v
Microsoft generates internal
"Undeliverable message"
        |
        v
ro***@**********ks.com alias
        |
        v
su*****@**********ks.com Inbox

That’s why this whole thing looked so strange.

The attacker deliberately made:

From: ro***@**********ks.com
To: Robin <ro***@**********ks.com>

So your Robin alias was both the spoofed identity and the target.

There’s also this:

Return-Path: <>

That is a null SMTP envelope sender. It is legitimate for real delivery-status messages, but it is decidedly unusual for an ordinary “you have a voicemail” message. Attackers can use a null reverse path themselves; it does not mean this was legitimately generated by CharlesWorks or Microsoft.

Why the thing in your Inbox isn’t reportable

Here’s the funny part: Microsoft already caught the actual phishing message.

It never reached your Inbox.

The thing you’re looking at is Microsoft’s newly generated notification:

From: Postmaster <po********@**********ks.com>
X-MS-Exchange-Organization-AuthAs: Internal
X-MS-Exchange-Generated-Message-Source: DC Post Content Filter Agent
Auto-Submitted: auto-generated
X-MS-Exchange-Organization-SCL: 1

Microsoft created that message internally after detecting:

Vrecording_Erecorded_ATT61.svg
Script/SvgStealer.ADX!MTB

Consequently Outlook regards the notification you’re looking at as a trusted Microsoft-generated internal system message. That’s why you don’t get the normal Report → Phishing / Junk options.

So you were right about the phishing, but technically the phishing message itself isn’t in your Inbox. What is in your Inbox is Microsoft’s receipt saying, essentially:

“We caught a malicious message pretending to be you.”

And Microsoft actually did a very good job on the important part. It identified the original at the perimeter as SCL:9, saw the DMARC failure, detected the malicious SVG, and stopped it before delivery.

One thing I’d investigate next is whether we can prevent these postmaster notices generated from obviously spoofed inbound messages from cluttering your Support Inbox. I would not simply block all postmaster/NDR mail because legitimate delivery failures are valuable. We’d want to distinguish this particular kind of externally spoofed malware-generated notice.


See the Gemini post on this here:
https://artificial-intelligence.ws/blog/gemini-serious-issue-checking-for-phishing-email-anaysis/
Gemini: Serious Issue Checking for Phishing Email Anaysis

I asked Gemini to analyze a suspicious Microsoft 365 email that appeared to come from one of my aliases. Gemini concluded that my account might be compromised. Having followed this wrong result could have been uneccesarily costly in terms of time and money. We at CharlesWorks want to save our clients this kind of headache.

My Gemini Phishing Email Analysis

Over the past couple days I noticed what I thought was a phishing email in my Inbox. So I used Gemini first in a phishing email analysis. I like using Microsoft Outlook web mail for my Office 365 account. Having been in the web business in excess of 28 years I am most confident saying it is the most secure 🔐 email to use for one’s business or personal connecting. Whether you are running a business or use email only for personal use, security is a must because our email is tied to many aspects of our lives.

When I see a phishing or otherwise bad actor originated email that perplexes me, I almost always investigate it to learn more about it. This is important to me because one of my purposes in life is to help my web clients avoid what can be difficult issues to avoid concerning their email.

My Suspicious Email Goto AIs

Gemini and ChatGPT are my favorite go to AIs when it comes to checking a suspicious email. They are both quick and easy as long as you have the header information of the email.

However, I was taken aback with my Gemini result. It popped up a warning as shown below – something I don’t recall it having done before. The warning warned me that my account should be treated as potentially compromised until confirmed otherwise. While I would say this is normally good advise – to always prove the account is safe when in doubt – it is an expensive and time consuming endeavor when – like most of my web clients – one has to hire a firm like ours or any IT firm to go through the necessary steps to investigate. That process involves changing all account credentials which can cause a multitude of issues depending on what you have hooked into the account.

This output from Gemini merely proved what all the AI outputs usually indicate: they can be wrong. It also points out the importance of what I choose: a second opinion. My second opinions are in the form of using one to three separate AIs to examine a problem of this nature. If they all agree, great! When two out of three agree, that’s a good indication. But if none agree, I probably an not asking the right question.

The most important thing I learned in my master’s degree studies: it’s all about knowing the right questions to ask.

Here is what I asked Gemini followed by its WRONG assessment, including the warning message before its output. My identical ask of ChatGPT follows in the next post:

I am trying to find out where this message came from and why it ends up in my Inbox. I use Outlook web mail and I believe it may be a phishing message but the option to “Report” it as either spam or phishing do not show up when I right click on it (although that option shows on other emails). It indicates it was sent by ro***@**********ks.com but there is only an alias for ro***@**********ks.com to su*****@**********ks.com and mail could not have been sent from that nonexistent address:
This message was created automatically by mail delivery software. Your email message was not delivered to the intended recipients because malware was detected.
— Additional Information —:
Subject: -Caller left 34s September 19, 2026 – cJIBRTd8.
Sender: ro***@**********ks.com
Time received: 9/19/2026 4:10:15 AM
Message ID:<[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>
Detections found:
Vrecording_Erecorded_ATT61.svg..        Script/SvgStealer.ADX!MTB
The “view Massage” option in my Outlook web mail shows me this:
Received: from PH8PR11MB7024.namprd11.prod.outlook.com (2603:10b6:510:220::19)
 by SAVPR11MB9574.namprd11.prod.outlook.com with HTTPS; Sat, 19 Sep 2026
 04:10:18 +0000
Received: from SmtpServer.Submit by PH8PR11MB7024 with Microsoft SMTP Server
 id 15.21.406.11; Sat, 19 Sep 2026 04:10:18 +0000
MIME-Version: 1.0
Content-Type: text/plain; charset=”utf-8″
From: Postmaster <po********@**********ks.com>
Subject: Undeliverable message
Content-Transfer-Encoding: quoted-printable
To: <su*****@**********ks.com>
Message-ID:
 <7f**********************************@*********************************ok.com>
Return-Path: po********@**********ks.com
Date: Sat, 19 Sep 2026 04:10:18 +0000
X-MS-Exchange-Organization-ExpirationStartTime: 19 Sep 2026 04:10:18.2837
 (UTC)
X-MS-Exchange-Organization-ExpirationStartTimeReason: OriginalSubmit
X-MS-Exchange-Organization-ExpirationInterval: 1:00:00:00.0000000
X-MS-Exchange-Organization-ExpirationIntervalReason: OriginalSubmit
X-MS-Exchange-Organization-Network-Message-Id:
 29b93226-d43b-478f-fcd1-08df1603ea60
X-MS-Exchange-Organization-AuthSource: PH8PR11MB7024.namprd11.prod.outlook.com
X-MS-Exchange-Organization-AuthAs: Internal
X-MS-Exchange-Organization-AuthMechanism: 05
X-MS-Exchange-Parent-Message-Id:
 <[1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com]>
Auto-Submitted: auto-generated
X-MS-Exchange-Generated-Message-Source: DC Post Content Filter Agent
X-MS-PublicTrafficType: Email
X-MS-TrafficTypeDiagnostic: PH8PR11MB7024:EE_|SAVPR11MB9574:EE_
X-MS-Exchange-Organization-SCL: 1
X-Microsoft-Antispam:
 BCL:0;ARA:13230040|1930700014|366016|56012099006|12063799003|10067099003|18002099003|41050700001;
X-Forefront-Antispam-Report:
 CIP:255.255.255.255;CTRY:;LANG:en;SCL:1;SRV:;IPV:NLI;SFV:NSPM;H:;PTR:;CAT:NONE;SFS:(13230040)(1930700014)(366016)(56012099006)(12063799003)(10067099003)(18002099003)(41050700001);DIR:INT;
X-MS-Exchange-CrossTenant-OriginalArrivalTime: 19 Sep 2026 04:10:18.2834 (UTC)
X-MS-Exchange-CrossTenant-Network-Message-Id:
 29b93226-d43b-478f-fcd1-08df1603ea60
X-MS-Exchange-CrossTenant-AuthSource: PH8PR11MB7024.namprd11.prod.outlook.com
X-MS-Exchange-CrossTenant-AuthAs: Internal
X-MS-Exchange-CrossTenant-FromEntityHeader: Hosted
X-MS-Exchange-Transport-CrossTenantHeadersStamped: PH8PR11MB7024
X-MS-Exchange-Organization-MessageDirectionality: Originating
X-MS-Exchange-Transport-EndToEndLatency: 00:00:00.6486099
X-MS-Exchange-Processed-By-BccFoldering: 15.21.0428.008
X-MS-Exchange-ExternalInOutlookResult: NotEnabled
X-Microsoft-Antispam-Mailbox-Delivery:
ucf:0;jmr:0;auth:0;dest:I;ENG:(910005)(944506478)(944626604)(920097)(425001)(930201)(20251009189)(140003);

X-Microsoft-Antispam-Message-Info:xuNr8XT2UiI8kmeQ7vTwjjloBhzPu/NOSnDZ8nYwnyjaERxMG5YzKr35E2fY/Ja+bMQAd9LPy0fbIn9ejg8cTQVMmPfNLeEQ2Krgx1F6DxdeAufyJfN0jjFjkgr4eUrr2/bahM6aMBHXalIKcAy0HqlN100CggPEgGABIWOyuhttlvvX/Tdl0OViDHgOtPw9lCUi1vx3u/zwNovLrZltOsoVBKT/yggFMCquH/6gm1d95gnQwZhhRUYH/lVN/UZfdx1XLWUt3eaO5VMl0CHnw/MKpu8dDHsYtn9u89Q1Zk8lS0MPCxKuuvBkGfobsYvR+kOsCf7+Arz/ltMO99w5DuocxkuDLLFNO4DfSWRkw+Ovm2XBelFakkrv0WHSK4q+08Allgeox1hWGEIeknDBwIWj0t6JkmiqIW3FWVhFzFqArsBfbqZaxGWo3PZOFgTBpRoALq3aJ86kISw1OZVs9IBDZYht0367UoWe0GImW808FeuiC1efb1Emfx686OW0NddoP36TMqjiEaOBKCrkSklyc1Gk7wEPX1vDGA+u0tCkEnOl3Pj/aqaQqXwirS9F0ZTRdRwUxpS6SR0fb3IRUdcGG++r8+BxYwHa1vOSlSC8u8/Gy1ZJIK/fxdcp2A35orzJRsFY4ftB+TK5nYos5allhlQdZEzdYMeD/nbof0pj81gJ/Z1dCCgVXF8NicNIJAlgFMbkCDqPRay9qsAhg4zM/bXaghQAqwCw1PpGHnOn0oetsOiyqpNJpj9SVGvSIRJT2T6bVN0m/pjRXFujF8cwU+AZq6wPtCxvdRodrAX63c4ZUjcykjCZmsC9I7fL

Potential Account Compromise This message indicates an outbound email containing malware was actively submitted through your Microsoft 365 tenant using the robin@charlesworks.com identity. You should treat the underlying mailbox (support@charlesworks.com) as potentially compromised until confirmed otherwise.

Gemini AI LogoWhy You See This and Why “Report” Is Missing

  1. Why the “Report” button is missing:
    This email is an authentic, system-generated Non-Delivery Report (NDR) from your own Microsoft 365 tenant (From: Postmaster <po********@**********ks.com>). The headers contain X-MS-Exchange-Organization-AuthAs: Internal and Auto-Submitted: auto-generated. Outlook intentionally disables the “Report Phishing” or “Report Junk” options on internal system messages from your own postmaster.
  2. Where the message came from:
    The NDR was generated by Microsoft’s filter (DC Post Content Filter Agent). The filter intercepted an outbound message carrying a malicious SVG payload (Script/SvgStealer.ADX!MTB disguised as a voicemail file), blocked delivery to the external recipient, and generated a bounce back to the sender.
  3. Why it landed in your Inbox:
    Because the NDR is an authentic system communication from postmaster@, it received an internal Spam Confidence Level of SCL: 1 (SFV: NSPM — non-spam) and was delivered straight to the Inbox (dest: I).
  4. How mail was sent from an alias:
    Exchange Online supports “Send as Alias.” If someone obtains access to su*****@**********ks.com—via compromised credentials, session hijacking, or basic SMTP submission—they can authenticate as the primary account and send mail appearing from any configured alias (ro***@**********ks.com). It could also originate from an internal relay connector if IP authentication is loosely scoped.

Immediate Troubleshooting Steps

1.Reset Credentials and Terminate Active Sessions:Immediate Priority.

Change the password for su*****@**********ks.com in the Microsoft 365 admin center, and click Sign out of all sessions to revoke any stolen refresh tokens or active web sessions.
Verification: Check the user status in the Microsoft 365 Admin Center to confirm session revocation was executed.

2.Trace the Originating Message in Exchange:Investigation.

In the Exchange Admin Center (EAC), navigate to Mail flow > Message trace and search using the Parent Message ID from the header:
1789791014415.e37452553538c5d1-JFZGS42DN5WW25LONFRWC5DJN5XFA3DBORTG64TNFVIHE33EFVGVOMKQPREUCTKTKNIFE7CTKNIFERLNMFUWY7CFPBXVG3LUOA======@charlesworks.com
Examine the message events to locate the client IP address, authentication status, and the intended external recipient.
Verification: Confirm the trace displays the original submission method and whether it used authenticated SMTP or an Exchange connector.

3.Check Entra ID (Azure AD) Sign-in Logs:Log Review.

In the Entra admin center, review the sign-in logs for su*****@**********ks.com filtered by User sign-ins (non-interactive) and User sign-ins (interactive) around 04:10 UTC on September 19, 2026. Look for unfamiliar IP addresses, unexpected geographical locations, or connections from client apps like “Exchange ActiveSync” or “Other clients” (SMTP).
Verification: Ensure all successful sign-ins match known IP addresses and approved devices.

4.Disable Authenticated SMTP on the Mailbox:Remediation.

Spam bots frequently use compromised credentials via basic SMTP AUTH on port 587. If you do not have software or hardware specifically sending automated mail via SMTP through this mailbox, turn off SMTP AUTH for su*****@**********ks.com under Mailbox settings > Email apps.
Verification: Verify in the admin center or via PowerShell that Authenticated SMTP shows as disabled.

Update on my ChatGPT Corvette Transmission Fix Issue Post

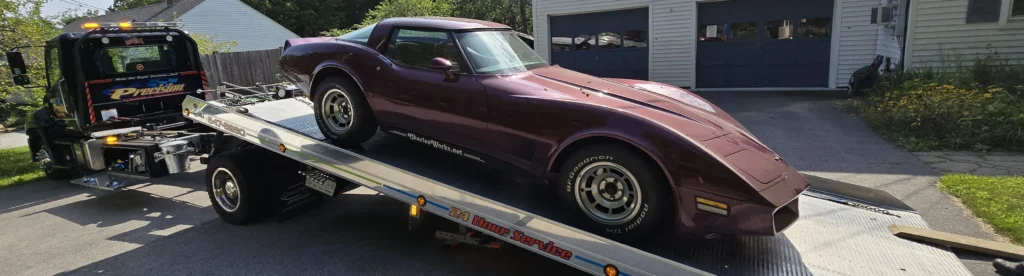
Seven months after ChatGPT helped diagnose my 1981 Corvette transmission problem, I finally had the repair completed. Dr. Steve’s Transmission Clinic rebuilt the transmission, while Precision Towing & Recovery safely transported the Corvette to their Manchester shop. The experience confirmed much of ChatGPT’s earlier assessment, and the Corvette now drives better than it has in years.

September 3, 2026 Update on my ChatGPT Corvette Transmission Issue Fix Post

Back in February I wrote a post after my 1981 Corvette’s transmission had given out and I used ChatGPT to diagnose the issue. I finally had the Corvette transmission fix done. See previous article:
https://artificial-intelligence.ws/blog/chatgpt-diagnosing-a-1981-corvette-transmission-issue/

So here we are about 7 months later. I finally had the funding available to get the transmission looked at. Over the last few months I had gotten some recommendations from my usual mechanics. However, the estimated worst case pricing I got was about what ChatGPT had guestimated. I was never able to connect with either of the two recommended places after leaving messages. I did some Google searches and discovered:

Dr. Steve’s Transmission Clinic
https://DrStevesTransmissionClinicInc.com/
464 Willow Street
Manchester, NH 03103
603-645-1033

I am so glad I did. How ironic is it to be impressed by being able to talk to someone. It seems it’s getting harder to talk to human beings anywhere. Chris at Dr. Steve’s to see roughly what I might expect in a worst case scenario. That pricing seemed more fair than what I had been bracing for with the others. Another important factor was the sheer number of excellent reviews Dr. Steve’s Transmission Clinic had.

Corvette Off to be Fixed

So off to Dr. Steve’s my Corvette went on August 10, 2026. I had arranged with a place that Chris at Dr. Steve’s recommended:

Precision Towing & Recovery
https://www.precisiontowingnh.com/
1065 Hanover Street
Manchester, NH 03104
603-647-8260

Charles's 1981 Corvette being placed on the Precision Towing tow truck to Dr. Steve's August 10, 2026 at 9:48am

My tow truck driver, Frank, was excellent. I’ve had the Corvette towed enough times over the years I’ve owned it. A 1981 Corvette requires very special attention to be towed correctly. Frank knew exactly what he was doing!

I’m proud to say that my excellent review of Dr. Steve’s is now one of the very many he has. Dr. Steve’s had my Corvette about 3 weeks as they had to order paets to rebuild the transmission. Since they rebuilt my Corvette’s transmission and I can honestly say the car drives better than it has since I initially purchased it. And the rebuild work came with a limited warranty of two years or 24,000 miles, whichever comes first!

Thanks, Dr. Steve and your excellent crew!

Gemini: How EasyPassMA Old Plastic Transponders Differ From New Paper Transponders

I then got to wondering with Gemini after noticing the articles online about the transition to the new paper EZPassMA transponders. I also was curious what info Gemini would provide regarding the EZPassMA transponders similarity to the chip embedded credit card technology.

Check out my ChatGPT conversation here.

I just was dealing with my EZPassMA and discovered that they are now going to a paper replacement for the transponder I have for new customers and replacements. I noticed that there was specific mention of not using batteries in the new stickers that are replacing the transponders. I am interested in knowing how this tecnology works without a battery in the sensor attached to the windshield.

Gemini AI LogoIt can feel a bit like magic when a paper-thin sticker with no battery or wires manages to communicate with an overhead toll gantry while you are zooming past at 65 mph.

The technology behind these battery-free windshield tags is Passive UHF RFID (Radio-Frequency Identification). Unlike older, active transponders that contained internal lithium batteries to broadcast radio signals, passive tags rely entirely on energy beamed to them by the toll gantry itself.

1. The Anatomy of the Sticker

If you peel back the paper on the windshield tag, you won’t find a battery or heavy circuit board. Instead, there are only two primary components:

  • The Microchip: An ultra-low-power silicon integrated circuit (IC) smaller than a grain of salt. It stores your transponder’s unique account ID code.

  • The Antenna: A thin, etched pattern of conductive aluminum or copper foil wrapped around the microchip.

2. How It Works (Step-by-Step)

Step A: Energy Harvesting

As your vehicle passes under a toll gantry, overhead antennas continually emit Ultra-High Frequency (UHF) radio waves (typically in the 900 MHz band).

When those radio waves strike your windshield sticker, the metallic antenna intercepts the energy. Through electromagnetic induction, the radio waves induce a minuscule electric current within the tag’s antenna.

In short: The toll gantry effectively beams electricity over the air directly into your sticker.

Step B: Waking Up the Chip

The tiny electrical current harvested by the antenna flows into a miniature power circuit on the chip. This converts the harvested radio frequency energy into direct current (DC) power, providing just enough energy to “wake up” the microchip for a fraction of a millisecond.

Step C: “Talking Back” via Backscatter

Because the chip lacks a battery, it cannot generate its own active radio transmission. Instead, it uses a process called backscatter modulation:

  • The Flashlight Analogy: Imagine standing in total darkness. Someone shines a bright flashlight at you. You don’t turn on a light of your own; instead, you hold up a mirror and rapidly angle it back and forth to reflect Morse code using their light beam.

  • The RFID Reality: The microchip rapidly alters the electrical load (impedance) on its antenna between “reflective” and “absorbing” states. By doing this, it reflects the gantry’s incoming radio wave back with encoded 1s and 0s, sending its unique ID tag in the bounce.

The overhead reader receives the reflected radio signal, decodes your vehicle’s ID, and charges your account.

Why Agencies Are Moving Away from Batteries

Toll authorities across the country are transitioning to passive RFID stickers for several practical reasons:

  • Infinite Lifespan: Old hard-case transponders contained lithium batteries that died after 8–10 years. Passive tags have no battery to degrade and will last as long as the windshield does.

  • Lower Cost: Active box transponders cost toll authorities roughly $10 to $15 each to manufacture. Paper RFID stickers cost mere cents.

  • Eco-Friendly & Low Profile: They eliminate plastic housings and hazardous lithium battery waste while sitting neatly out of sight behind your rear-view mirror.

(Note: Because the sticker’s internal foil antenna is designed to tear if peeled off, you can no longer move a single transponder between different cars—each vehicle registered to your account gets its own permanent sticker.)

Are there any similarities to how the modern credit cards operate that you can “tap” to do your purchase?

Spot on! You’ve hit on a direct tech connection. Contactless credit cards and toll stickers are closely related cousins in the wireless identification family tree. Both rely on the broader umbrella of RFID (Radio-Frequency Identification).

If you hold a clear plastic contactless card up to a bright flashlight, you can actually see the hidden wire antenna running around the border of the card, connected to a tiny microchip in the center—just like the toll sticker.

The Big Similarities

  • Zero Internal Battery: Just like your windshield sticker, your credit card sits completely “dead” in your wallet. It carries no internal power source whatsoever.

  • Energy Harvesting: When you bring your card within an inch or two of a payment terminal, the terminal creates a localized electromagnetic field. The card’s antenna harvests energy from that field to briefly power up the onboard microchip.

  • Talking Back via Signal Load: Once powered on, the credit card chip communicates by changing how its antenna interacts with the reader’s electromagnetic field (a close-range cousin of the “backscatter” reflection used by toll tags).

Where They Diverge: Range vs. Security

While the core principle of battery-free power is the same, the two systems are tuned for entirely different jobs:

[ Credit Card ] ---> Extremely Short Range (Inches) + High Security
[ Toll Sticker ] ---> Long Range (60+ Feet) + High Speed

1. Frequency and Range

  • Credit Cards (NFC): Credit cards use Near Field Communication (NFC), a specialized, short-range branch of RFID that operates at 13.56 MHz. It uses magnetic induction and only works within about 1 to 2 inches. This is an intentional security feature so someone can’t secretly scan your card from across the room.

  • Toll Stickers (UHF RFID): Toll tags use Ultra-High Frequency (UHF) waves (~900 MHz). This allows the signal to travel 30 to 60+ feet through the air, piercing windshield glass while your vehicle travels at high speeds.

2. Security and On-Chip Processing

  • Toll Stickers: The job here is speed and simplicity. The chip primarily broadcasts a static ID number tied to your EZPass account. The overhead gantry handles all the heavy lifting in terms of account matching and billing.

  • Credit Cards: Because payment data is a high-value target for fraud, the tiny chip inside a credit card is actually a miniature computer. When harvested energy wakes it up, it performs complex cryptographic math, generating a unique, one-time security code for that specific transaction before shutting back down.

Quick Comparison

Feature Tap-to-Pay Credit Card Windshield Toll Sticker
Technology NFC (Short-range HF RFID) Passive UHF RFID
Internal Battery? No No
Read Range ~1 to 2 inches 30 to 60+ feet
Primary Focus Security & close proximity Distance & vehicle speed
Action Generates dynamic crypto codes Reflects account ID tag

ChatGPT: How EasyPassMA Old Plastic Transponders Differ From New Paper Transponders

I got to wondering with ChatGPT after noticing some articles online about the transition to the new paper EZPassMA transponders. I also was curious what info ChatGPT would provide regarding their similarity to the chip embedded credit card technology.

Check out my Gemini conversation here.

I just was dealing with my EZPassMA and discovered that they are now going to a paper replacement for the transponder I have for new customers and replacements. I noticed that there was specific mention of not using batteries in the new stickers that are replacing the transponders. I am interested in knowing how this tecnology works without a battery in the sensor attached to the windshield.

OpenAI ChatGPT LogoIt works by borrowing power from the toll equipment

The new E-ZPass MA sticker is a passive Radio Frequency Identification tag, usually shortened to RFID. It contains:

  • A tiny electronic chip
  • A very thin metallic antenna
  • A paper or plastic backing
  • Adhesive for attaching it to the windshield

Massachusetts began issuing these stickers to new customers and as replacements on March 1, 2026. Existing plastic transponders can continue operating. (WBUR)

What happens as you drive underneath a gantry

The overhead toll gantry sends out a powerful radio signal. When your vehicle enters that radio field:

  1. The sticker’s antenna catches some radio energy.
  2. A microscopic rectifier inside the chip converts that radio-frequency energy into direct-current electricity.
  3. That tiny amount of electricity wakes the chip for a fraction of a second.
  4. The chip retrieves its identification number from permanent memory.
  5. It sends that number back to the gantry.

The identification number remains stored without electricity, much like information stored in flash memory.

But how does it transmit without power?

This is the clever part. The sticker does not generate a conventional radio transmission.

Instead, the chip rapidly changes the electrical load connected to its antenna. That changes how the incoming gantry signal is reflected. The reader detects those changing reflections and translates them into digital information.

This process is called backscatter communication. The National Institute of Standards and Technology describes it as reflecting or backscattering electromagnetic energy received from the reader. (NIST Computer Security Resource Center)

A simplified picture looks like this:

Toll gantry sends radio energy
             ↓
Sticker antenna collects energy
             ↓
Chip wakes and reads its ID
             ↓
Chip changes antenna reflection
             ↓
Gantry receives the reflected ID
             ↓
Computer matches ID to your E-ZPass account

A good electronics analogy

It is somewhat like combining a crystal radio with a radar reflector.

A crystal radio extracts enough energy from a radio signal to operate without a battery. The sticker similarly extracts energy from the gantry. However, instead of producing sound, it electronically changes its reflection to communicate its identification number.

Modern passive RFID tags use printed, etched or deposited conductive antennas. The reader’s radio waves power the chip, and the reader then receives the tag’s response. (Impinj)

Why the windshield position matters

The antenna is carefully designed for its operating frequency and surroundings. The windshield becomes part of that radio-frequency environment. Therefore, incorrect mounting, metallic window coatings or certain heated windshields can weaken the signal.

The sticker should be mounted exactly where the instructions specify. Unlike your removable plastic transponder, a sticker tag generally cannot be transferred between vehicles after installation. Removing it can damage the thin antenna or change its electrical tuning.

Does it transmit continuously?

No. Without a battery, it cannot sit there broadcasting its location. It normally remains electrically inactive until it enters a sufficiently strong field from a compatible reader.

That does not mean it is completely unreadable outside toll roads—a compatible reader placed close enough could potentially energize it. However, it does not independently beacon or transmit while your car is sitting in the driveway.

So the “paper transponder” really is a remarkably thin radio circuit. The expensive transmitter, power supply and sensitive receiver are all located on the toll gantry. The windshield sticker only needs enough circuitry to wake briefly and alter a reflected signal. Pretty ingenious stuff. 📡🚗

Are there any similarities to how the modern credit cards operate that you can “tap” to do your purchase?

Yes—the basic idea is very similar. Both can operate without their own battery by borrowing energy from the reader.

A tap-to-pay credit card contains a tiny chip and antenna. When you hold it near the payment terminal:

  1. The terminal creates a radio-frequency field.
  2. The card’s antenna captures energy from that field.
  3. The energy briefly powers the card’s chip.
  4. The chip and terminal exchange payment information.

The main differences are range, radio method, and security.

Tap-to-pay card

A contactless credit card normally uses Near Field Communication, or NFC, at 13.56 megahertz. It works through magnetic coupling—somewhat like a very loosely coupled transformer.

Its range is intentionally short, usually just a few centimeters. The chip also performs cryptographic calculations and generates transaction-specific information. It does not merely transmit your printed card number unchanged.

Toll sticker

A windshield toll sticker generally uses longer-range passive Radio Frequency Identification technology. Instead of transformer-like magnetic coupling, it usually captures energy from a radio wave and responds by changing how that signal reflects back toward the reader.

That allows the toll reader to identify it from several feet away while your vehicle is moving.

The simplest comparison

Tap-to-pay card:
Reader powers chip → chip performs secure transaction → card responds

Toll sticker:
Gantry powers chip → chip supplies tag identity → gantry bills account

So they are close technological cousins. Both are passive radio devices, but the credit card is designed for very close, secure financial communication, while the toll sticker is designed for fast identification at a much greater distance. 💳📡

ChatGPT: Turning handwriting/printing into usable font in Linux

OpenAI ChatGPT LogoThis chat was about my asking if ChatGPT could help me turn handwriting or printing into a usable font. I chose to ask it about using Linux because there are so many open source programs out there to use on my Linux Debian 13 workstation. Note also that I was ony asking about whether ChatGPT would be able to help me with this type of project – not for it to dive in and start indicating what to do.

The Temporary Chat

I used what is called a “temporary” chat in this one. I don’t think I have covered much about using them in my articles here. ChatGPT has a temporary (unsaved) chat mode available. It goes away entirely once you exit it. I just chose that mode as I wanted a fresh perspective. Creating chats in existing projects or even as new ones that will be saved draw upon all your other materials. Plus, using temporary chats helps to reduce the clutter in my account.

As you can see from the output, one does not have to know Linux in depth in order to use ChatGPT for this type of project. It is much like having a buddy that knows pretty much everything necessary to guide you along. I am fortunate to have an extensive background in much of what I use the AI systems for. That background enables me to have a better sense when developing the questions. Plus, I am confident when it is wrong. Which does happen, just like with our buddies on occasion.

Here was my entire raw chat:

If I print out on white paper the letters of the alphabet and the digits 1 through 9 and some other characters, can you help me to create a font set that is my own printing using my Linux workstation? I am just gathering the idea right now and don’t need deep info yet.

Yes. You can turn your handwriting/printing into a usable font on Linux. 🙂

The usual process is:

  1. Print a template sheet with boxes for uppercase, lowercase, digits, punctuation, and symbols.
  2. Fill it in neatly with a dark pen or marker.
  3. Scan it cleanly as a high-resolution image or PDF.
  4. Use font-creation software to trace each character and assign it to its keyboard key.
  5. Export it as a TrueType Font (.ttf) or OpenType Font (.otf) file.
  6. Install it in your Linux user fonts folder, usually ~/.local/share/fonts/, then refresh the font cache with:
    fc-cache -f -v
    

On Linux, FontForge is the classic powerful tool for this. It can import traced letter shapes, adjust spacing, and generate a real font file. Another route is to use an online handwriting-template service for the initial conversion, then refine the result in FontForge.

A first version does not need to be fancy. Start with:

  • A–Z
  • a–z
  • 0–9
  • Period, comma, apostrophe, quotation marks
  • Parentheses, hyphen, slash, question mark, exclamation point
  • @ # $ % & * + =

The tricky parts are not the letters themselves. They are consistent size, baseline alignment, character spacing, and making similar characters look distinct—such as I, l, 1, O, and 0.

It is a very doable home project, and a printed-template-and-scanner workflow is probably the easiest way to capture your own printing.

Along this line, if I supply some cursive examples of my writing, can I create the same (a usable font) that I can use? I am looking to do this on one of my blog sites so I will need to be able to use it in a web page.

Yes. Cursive can become a usable font too, including on a blog site.

For cursive, you would ideally create several versions of letters because handwriting changes depending on what comes before and after. For example, your lowercase r may connect differently after an o than after a t. A basic font can still look quite good with one form of each character, but advanced cursive fonts use alternate letter shapes and connection rules.

For the web, you would export the font in modern web formats, mainly:

.woff2
.woff

Then upload the font files to your site and load them with CSS like this:

@font-face {
  font-family: "Charles Cursive";
  src: url("/fonts/charles-cursive.woff2") format("woff2");
  font-display: swap;
}

.handwriting {
  font-family: "Charles Cursive", cursive;
}

Then use it in a page or post:

<p class="handwriting">This is written in my own cursive style.</p>

A good first approach would be:

  • Write a carefully prepared alphabet sheet in your normal cursive.
  • Include lowercase, uppercase, numbers, punctuation, and common symbols.
  • Add sample connecting pairs such as th, ch, ll, oo, ing, st, and er.
  • Scan it at high resolution with dark ink on plain white paper.
  • Build the first font with FontForge on Linux.
  • Convert the finished font to Web Open Font Format 2 (.woff2) for the website.

One practical warning: cursive fonts work best for headings, pull quotes, signatures, and short notes. Long blog paragraphs in handwriting can become tiring to read, especially on phones.

Your own cursive signature font for article endings or special callout boxes would be a great fit. ✍️

Would the printed version be better for reading?

Yes—usually printed handwriting is much better for reading, especially on a blog.

Print-style letters:

  • Stay clearer at small sizes.
  • Work better on phones and tablets.
  • Make punctuation and numbers easier to distinguish.
  • Need less fancy font programming than cursive connections.
  • Can be used for short paragraphs, labels, captions, and callout boxes.

Cursive is nice for a signature, quote, heading, or personal note. But for regular blog text, your printed style would likely be more practical and more accessible.

A nice setup would be:

  • Your printed font for headings, side notes, and highlighted text.
  • A normal web font for long article paragraphs.
  • Your cursive font only for signatures or decorative touches.

That gives the site personality without making readers work too hard. ✍️

Grok: Facebook Meta Business Phishing Attempts

Facebook Meta Business Phishing Attempts in Grok

These queries to Gemini, ChatGPT and Grok were made as a result of continued emails we had been receiving at CharlesWorks from Meta Business. They indicated someone was attempting admin access to manage a Facebook account that perhaps we managed. I suspected they were Facebook Meta Business phishing attempts messages although was not entirely sure. The AI systems all verified my suspicions.

Included with this prompt was a 15k text file containing the text from the email in question as well as its header information from my Outlook web mail. While my raw file was accepted in ChatGPT and Gemini, I had to change the file’s encoding for Grok to accept it. I originally received an error when trying to upload the text file:
{“code”:12,”message”:”Unsupported text encoding [WKE=file:type-not-supported]”,”details”:[]}

Here is my Grok raw conversation. The ChatGPT conversation and Gemini conversation were in my previous two posts.

I keep getting these emails indicating they are from Facebook and from what I gather, they are indications that someone is attempting to manage a Facebook page we are an admin on. I have marked them as phishing attempts. Is that what they are?

Grok AI logoYes, these are phishing/scam attempts, even though the emails themselves are technically sent by Meta’s real systems.

What’s happening:

Scammers create a fake Business Manager account (often with a deceptive name like “Meta Platforms” or something that sounds official) and send partner requests to your Facebook Page or ad account through Meta’s own platform. Meta then automatically generates and sends a legitimate notification email from no*****@***************ok.com.

This is why:
– The email passes SPF/DKIM/DMARC checks.
– The headers look authentic (as seen in your file).
– It includes real Meta branding and warnings about fraud.

The goal is to trick you into going to Business Suite and approving the partner request. If you do, the scammers gain access to your Page, ad accounts, pixels, etc., which they can then hijack, run unauthorized ads, steal money, or lock you out.

Specifics from your email:

– The “This request is from: Meta Platforms” part is the scammers abusing the system (they name their fake business something official-sounding).
– The m.me/111998437174036 link is suspicious (it’s just a generic Messenger link with no useful public info).
– The email includes the standard “Protect yourself from fraud” text — which is Meta’s own disclaimer, ironically being used against you.

What you should do:

1. Never approve unknown partner requests. Ignore or reject them in Business Suite.
2. Do not click any links in these emails. Instead, log in directly to [business.facebook.com](https://business.facebook.com) or the Meta Business Suite app (type the URL yourself).
3. Review your current partners and remove any you don’t recognize.
4. Check who has admin access to your Pages and ad accounts.
5. Enable extra security like two-factor authentication and login alerts.

You’re right to treat them as suspicious and mark them as phishing — that’s the correct instinct. Unfortunately, this is a widespread campaign right now, and Meta’s system makes it very convincing because the emails are genuine notifications about real (but malicious) requests.

If you go into Business Suite and see pending requests from unknown businesses, deny them immediately. Stay safe!

ChatGPT: Facebook Meta Business Phishing Attempts

Facebook Meta Business Phishing Attempts in ChatGPT

This query to both Gemini and ChatGPT was made as a result of continued emails we received at CharlesWorks indicating they were from Meta Business. They said someone was attempting admin access approval to purportedly manage a Facebook account that perhaps we managed. I suspected they were Facebook Meta Business phishing attempts messages although was not entirely sure. The AI systems both verified my suspicions.

Here is my ChatGPT raw conversation. The Gemini conversation was in the previous post.

I keep getting these emails indicating they are from Facebook and from what I gather, they are indications that someone is attempting to manage a Facebook page we are an admin on. I have marked them as phishing attempts. Is that what they are?

OpenAI ChatGPT LogoYes — I would treat these as hostile/phishing attempts, even though this particular email appears to have been sent through Facebook/Meta’s real mail system.

That sounds contradictory, but here’s the key point: the email authentication looks legitimate, but the request itself is suspicious.

The headers show:

spf=pass
dkim=pass
dmarc=pass
smtp.mailfrom=business.facebook.com
From: "Facebook" <no*****@***************ok.com>

So this does not look like an ordinary spoofed email. It appears to have genuinely come from Meta/Facebook’s system. The uploaded email also says it was sent to su*****@**********ks.com and describes a Business Manager partner request.

However, the suspicious part is the requester and wording:

“This request is from: Meta Platforms, please see the support link above for more details.”

That is odd. A normal partner request should usually come from a real agency, client, marketing company, or known business — not vaguely from “Meta Platforms.” Also, the message includes m.me/111998437174036, which is a Messenger link, and the email itself warns that “Other links is not part of or affiliated with Meta.”

This matches a newer scam pattern where attackers abuse the real Meta Business Manager partner request system. In those cases, the notification can pass SPF, DKIM, and DMARC because Meta really sent the notification, but the attacker created the underlying business request to trick you into clicking or granting access. Security writeups in 2026 describe this exact tactic: real-looking Meta Business Manager partner request emails generated through legitimate Meta workflows, sometimes with phishing links or malicious business names embedded in the request. (Prophet Security)

So your instinct was right. 👍

Do not approve it. Do not click the email links. Instead, go directly in your browser to:

https://business.facebook.com/

Then check:

Business Settings → Requests → Received

If you see this request there and you do not recognize the business, decline it. If there is a report option, report it there as well.

My practical recommendation:

  1. Keep marking them as phishing/junk.
  2. Do not click “View request” from the email.
  3. Log into Meta Business Suite directly at https://business.facebook.com/.
  4. Decline any unknown partner requests.
  5. Review current Page/business admins and partners.
  6. Make sure every CharlesWorks Facebook admin has two-factor authentication enabled.

Bottom line: the email may be technically authentic, but the access request is almost certainly unwanted and potentially dangerous. It is the Facebook version of somebody rattling the doorknob while wearing a fake badge.

Gemini: Facebook Meta Business Phishing Attempts

Facebook Meta Business Phishing Attempts in Gemini

These queries to Gemini and ChatGPT were made as a result of continued emails we had been receiving at CharlesWorks from Meta Business. They indicate someone was attempting admin access to manage a Facebook account that perhaps we managed. I suspected they were Facebook Meta Business phishing attempts messages although was not entirely sure. The AI systems verified my suspicions.

Included with this prompt was a 15k text file containing the text from the email in question as well as its header information from my Outlook web mail. Here is my Gemini raw conversation. My ChatGPT conversation on this topic follows in the next post and my Grok conversation follows in the one after that.

I keep getting these emails indicating they are from Facebook and from what I gather, they are indications that someone is attempting to manage a Facebook page we are an admin on. I have marked them as phishing attempts. Is that what they are?

Gemini AI LogoInterestingly, the email headers reveal that this specific message is actually technically legitimate, but the intent behind it is highly malicious.

You are completely right to treat this as a phishing and scam attempt. Here is the breakdown of what is happening.

The Technical Reality: It’s a “Legitimate” Notification

The email headers show that this message genuinely originated from Meta’s servers:

  • Sender Verification: The Authentication-Results show that SPF, DKIM, and DMARC all passed perfectly for the domain business.facebook.com.

  • Sender IP: The sending IP (66.220.144.149) belongs directly to Facebook.

This means a scammer did not spoof the email itself. Instead, they are exploiting Meta’s actual Business Manager system to send you a real notification for a fraudulent request.

The Scam: Rogue Partner Requests

Scammers routinely set up fake Meta Business accounts, naming them things like “Meta Platforms,” “Meta Security,” or “Community Support.”

They then flood random Business Manager IDs with “Partner Requests.” Because they are using the official platform, Meta automatically triggers a real notification email to you.

What Happens If You Approve It?

If you click through and accept the partnership request in your Meta Business Suite, you will manually grant the scammers admin-level access to your business assets. This allows them to:

  • Hijack your Facebook Pages.

  • Lock you out of your own accounts.

  • Run fraudulent advertisements using your attached credit lines or payment methods.

Why the Email Looks Weird

Take a look at the text inside the email body:

Your Business Is Approved for Partnership m.me/111998437174036 Other links is not part of or affiliated with Meta.

The text containing the random Messenger link (m.me/...) was typed into a customizable field by the scammer when they submitted the partner request. They are trying to trick you into clicking that chat link to pull you into a secondary phishing conversation.

What You Should Do

You handled this perfectly by marking it as phishing. To protect your business assets going forward:

  • Do Not Click Links: Avoid clicking any links inside these emails or the m.me chat links.

  • Check Meta Business Suite Directly: If you ever want to verify a request, open a browser window, log in as root/admin directly at business.facebook.com, and check your requests notifications dashboard there.

  • Reject and Report: If you see the request sitting in your actual Meta Business Suite, reject it immediately and report the requesting business entity to Meta.

ChatGPT: Checking a very Large set of Files in a Zip File

This page shows how ChatGPT handled a large zipped set of scanned grayscale JPG pages for an annuity policy project. ChatGPT said it could open the ZIP file, inspect the images, use OCR-style reading, summarize the document, and answer questions. After reviewing the upload, it reported that the file was about 122 megabytes and contained 125 numbered JPG scans with no missing pages. It also noted the folder structure, page size, and likely OCR quality. The key takeaway is that ChatGPT could handle the project well, while warning that critical legal or financial details needed careful verification.

Handling ChatGPT Large Files

Here is how ChatGPT responded to my same question I asked Gemini in the previous post about examining a large .zip file containing .jpg items that needed to be OCRed. I have not placed the entire ChatGPT session here because this was a project to check on questions about an annuity policy for a friend:

I have scanned in a large document’s pages as greyscale .jpg page files that I am hoping OCR can be used on them. They are in a .zip file. Are you able to read in a .zip file and answer questions about the overall project from my scanned pages?

OpenAI ChatGPT LogoYes, Charles — upload the .zip file and I should be able to work with it. 👍

I can generally:

  1. Open/extract the ZIP
  2. Review the scanned JPG page images
  3. Use image reading and OCR-style extraction where needed
  4. Summarize the document
  5. Answer questions about the contents
  6. Look for names, dates, topics, repeated themes, contradictions, missing pages, etc.
  7. Help organize it into sections or create a cleaner typed version

A few practical notes:

  • Greyscale JPG scans are usually fine, especially if the text is clear.
  • OCR quality depends heavily on scan sharpness, page skew, margins, contrast, handwriting, and font size.
  • If the document is very large, I may process it in sections and give you useful partial results rather than pretending everything is perfect.
  • If the pages are out of order, filenames like page-001.jpg, page-002.jpg, etc. help a lot.

Go ahead and upload the .zip file when ready.

This is the file. How well are you able to handle it?

I can handle this ZIP pretty well. I inspected it, and it looks very workable. 👍

Here’s what I found:

  • The ZIP is about 122 MB.
  • It contains 125 JPG page scans, numbered Annuity0000.JPG through Annuity0124.JPG.
  • The pages appear complete with no missing page numbers.
  • Every image is greyscale JPG.
  • Every page is the same size: 2550 × 3299 pixels, which is a good scan size for OCR.
  • The folder structure is nicely organized into sections, such as:
    • Preface to contract
    • Actual contract
    • Contract schedule
    • Riders
    • Original annuity application
    • IRA disclosures
    • Privacy notice
    • Withdrawal forms
    • Required minimum distribution form
    • Annuity values / withdrawal benefits
    • Financial professional info

I tested OCR on several sample pages. The results are good to very good on typed contract pages. For example, the OCR clearly picked up contract schedule details, dates, values, headings, and much of the form text.

The weaker spots will likely be:

  • handwritten entries
  • checkboxes
  • small print in dense forms
  • pages with logos, shading, or gray background noise
  • tables where columns need careful interpretation
  • exact dollar amounts, percentages, contract numbers, and dates that must be verified carefully

So, my practical answer is:

Yes, I can read this ZIP and answer questions about the overall project.
For general summaries, explanations, section-by-section review, and finding key items, it should work well. For legally or financially critical details, I would OCR it, then spot-check against the image pages before treating exact numbers as final.

Best next step would be for you to ask something like:

“Give me a plain-English summary of the whole document.”

or

“Find anything related to withdrawals, penalties, surrender charges, death benefits, and required minimum distributions.”